• About
  • FAQ
  • Earn Bitcoin while Surfing the net
  • Buy & Sell Crypto on Paxful
Newsletter
Approx Foundation
  • Home
    • Home – Layout 1
  • Bitcoin
  • Ethereum
  • Regulation
  • Market
  • Blockchain
  • Business
  • Guide
  • Contact Us
No Result
View All Result
  • Home
    • Home – Layout 1
  • Bitcoin
  • Ethereum
  • Regulation
  • Market
  • Blockchain
  • Business
  • Guide
  • Contact Us
No Result
View All Result
Approx Foundation
No Result
View All Result
Home Business

Injective NPM Package Hacked to Steal Crypto Wallet Keys

approx by approx
July 10, 2026
in Business
0
Injective NPM Package Hacked to Steal Crypto Wallet Keys
189
SHARES
1.5k
VIEWS
Share on FacebookShare on Twitter


Hackers compromised a widely used Injective software package in a supply chain attack with malware designed to steal crypto wallet private keys, adding to a growing attack vector involving attackers using legitimate platforms to deliver malicious payloads.

Security firm Socket discovered on Thursday that a popular npm (node package manager) package with around 50,000 weekly downloads used for building on the Injective blockchain was maliciously modified to steal wallet private keys and seed phrases.
Related articles

Coinbase Faces Greater CLARITY Act Exposure, Saxo Says

Coinbase Faces Greater CLARITY Act Exposure, Saxo Says

September 16, 2026
Anchorage Adds Etherlink, Tokenized Uranium Custody

Anchorage Adds Etherlink, Tokenized Uranium Custody

September 16, 2026

The large number of downloads makes the incident “significant for developers and applications that handle Injective wallet workflows,” Socket researchers said. The malicious code has since been removed.

The software supply chain attack is a relatively new attack vector in which hackers don’t target a blockchain’s cryptography or smart contracts directly, but instead compromise trusted developer tools used to build wallets, exchanges and apps.

Injective is an interoperable layer 1 designed for DeFi applications. Its usage has dwindled over the past two years, with total value locked shrinking by 88% to current levels of $8.2 million from its $71 million peak in mid-2024, according to DefiLlama. 

Secretly copying private keys and phrases

Version 1.20.21 of the @injectivelabs/sdk-ts npm package was modified through a compromised developer GitHub account, with suspicious commits beginning June 8. It was also pinned across 17 other packages in the Injective Labs npm scope, “exposing users who may not have installed the SDK [software development kit] directly,” Socket said.

“The malicious release hooks wallet key-derivation functions, records private keys and mnemonics, and exfiltrates them through fake telemetry,” Socket explained. 

The malicious code hooked into normal functions used to generate wallet keys, and whenever a developer’s app used these functions, it secretly copied the seed phrase or private key. The compromised data was then encoded and sent to a web address that looked like a legitimate Injective network server.

“Any keys or mnemonics passed through affected packages should be treated as compromised,” Socket added. 

Related: ‘TrapDoor’ malware targets crypto dev tools in supply chain attack

Socket reported that the developer whose account was infiltrated quickly detected the compromise, but the malware had been downloaded more than 300 times, and “the campaign itself isn’t yet fully contained.”

Injective CEO Eric Chen said, “it’s already fixed, and the affected versions on npm are already deprecated.” No funds on the network are at risk, he added, and Socket did not specify whether any funds were stolen in the incident. 
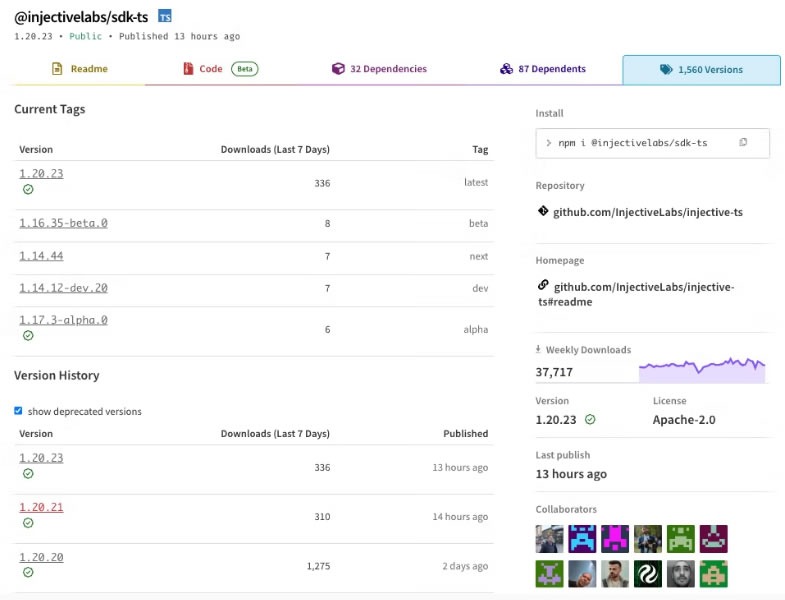
The compromised npm package was downloaded 310 times. Source: Socket

Wallet compromises most costly this year

The Security Alliance (SEAL) said in its second-quarter threat report that attackers are increasingly using legitimate platforms like GitHub, npm and Google to deliver payloads.

“In some cases, compromised systems are being used to push malicious code directly into a company’s own GitHub repositories, turning a single compromise into a distribution channel for the next one.”

SEAL added that the malware itself has also gotten more comprehensive, “with cross-platform payloads, including a rise in macOS-specific campaigns, that combine infostealers, RATs (remote access trojans) and backdoor capabilities in a single package.”

A similar supply chain attack hit Axios npm releases in March, while a malware campaign called TrapDoor was discovered in May targeting crypto, DeFi, AI and security developers.

GitHub itself was exploited on May 20 when it reported unauthorized access to its internal repositories following the compromise of an employee’s device. 

Wallet compromises were the most costly attack vector in the first half of 2026, with $444 million stolen across 33 incidents, CertiK reported Monday. 

Features: Bitcoin’s quantum dilemma: Bigger blocks or STARK proofs?


Source link

Share76Tweet47

Related Posts

Coinbase Faces Greater CLARITY Act Exposure, Saxo Says

Coinbase Faces Greater CLARITY Act Exposure, Saxo Says

by approx
September 16, 2026
0

While Bitcoin and crypto-linked stocks fell sharply after the US Senate failed to advance the Digital Asset Market Clarity, or...

Anchorage Adds Etherlink, Tokenized Uranium Custody

Anchorage Adds Etherlink, Tokenized Uranium Custody

by approx
September 16, 2026
0

Anchorage Digital Bank, the first federally chartered crypto bank in the US, has added custody support for Etherlink and seven...

Circle Launches Arc Mainnet With USDC Gas

Circle Launches Arc Mainnet With USDC Gas

by approx
September 16, 2026
0

USDC issuer Circle has launched the mainnet of Arc, a layer-1 (L1) blockchain targeting stablecoin payments and financial markets, particularly...

Revolut ID thefts highlight KYC’s dangers: Here’s how to fix it

Revolut ID thefts highlight KYC’s dangers: Here’s how to fix it

by approx
September 16, 2026
0

Zero-knowledge technology could let companies verify who you are without storing your identity documents. So why isn’t it already standard...

Bernstein Expects ‘Aggressive’ Rulemaking from SEC, CFTC, Following CLARITY Act Failure

Bernstein Expects ‘Aggressive’ Rulemaking from SEC, CFTC, Following CLARITY Act Failure

by approx
September 16, 2026
0

Bernstein analysts expect “aggressive and swift” rulemaking from the US Securities and Exchange Commission (SEC) and Commodity Futures Trading Commission...

Load More

youssufi.com

sephina.com

[vc_row full_width="stretch_row" parallax="content-moving" vc_row_background="" background_repeat="no-repeat" background_position="center center" footer_scheme="dark" css=".vc_custom_1517813231908{padding-top: 60px !important;padding-bottom: 30px !important;background-color: #191818 !important;background-position: center;background-repeat: no-repeat !important;background-size: cover !important;}" footer_widget_title_color="#fcbf46" footer_button_bg="#fcb11e"][vc_column width="1/4"]

We bring you the latest in Crypto News

[/vc_column][vc_column width="1/4"][vc_wp_categories]
[/vc_column][vc_column width="1/4"][vc_wp_tagcloud taxonomy="post_tag"][/vc_column][vc_column width="1/4"]

Newsletter

[vc_raw_html]JTNDcCUzRSUzQ2RpdiUyMGNsYXNzJTNEJTIydG5wJTIwdG5wLXN1YnNjcmlwdGlvbiUyMiUzRSUwQSUzQ2Zvcm0lMjBtZXRob2QlM0QlMjJwb3N0JTIyJTIwYWN0aW9uJTNEJTIyaHR0cHMlM0ElMkYlMkZhcHByb3gub3JnJTJGJTNGbmElM0RzJTIyJTNFJTBBJTBBJTNDaW5wdXQlMjB0eXBlJTNEJTIyaGlkZGVuJTIyJTIwbmFtZSUzRCUyMm5sYW5nJTIyJTIwdmFsdWUlM0QlMjIlMjIlM0UlM0NkaXYlMjBjbGFzcyUzRCUyMnRucC1maWVsZCUyMHRucC1maWVsZC1maXJzdG5hbWUlMjIlM0UlM0NsYWJlbCUyMGZvciUzRCUyMnRucC0xJTIyJTNFRmlyc3QlMjBuYW1lJTIwb3IlMjBmdWxsJTIwbmFtZSUzQyUyRmxhYmVsJTNFJTBBJTNDaW5wdXQlMjBjbGFzcyUzRCUyMnRucC1uYW1lJTIyJTIwdHlwZSUzRCUyMnRleHQlMjIlMjBuYW1lJTNEJTIybm4lMjIlMjBpZCUzRCUyMnRucC0xJTIyJTIwdmFsdWUlM0QlMjIlMjIlM0UlM0MlMkZkaXYlM0UlMEElM0NkaXYlMjBjbGFzcyUzRCUyMnRucC1maWVsZCUyMHRucC1maWVsZC1lbWFpbCUyMiUzRSUzQ2xhYmVsJTIwZm9yJTNEJTIydG5wLTIlMjIlM0VFbWFpbCUzQyUyRmxhYmVsJTNFJTBBJTNDaW5wdXQlMjBjbGFzcyUzRCUyMnRucC1lbWFpbCUyMiUyMHR5cGUlM0QlMjJlbWFpbCUyMiUyMG5hbWUlM0QlMjJuZSUyMiUyMGlkJTNEJTIydG5wLTIlMjIlMjB2YWx1ZSUzRCUyMiUyMiUyMHJlcXVpcmVkJTNFJTNDJTJGZGl2JTNFJTBBJTNDZGl2JTIwY2xhc3MlM0QlMjJ0bnAtZmllbGQlMjB0bnAtcHJpdmFjeS1maWVsZCUyMiUzRSUzQ2xhYmVsJTNFJTNDaW5wdXQlMjB0eXBlJTNEJTIyY2hlY2tib3glMjIlMjBuYW1lJTNEJTIybnklMjIlMjByZXF1aXJlZCUyMGNsYXNzJTNEJTIydG5wLXByaXZhY3klMjIlM0UlQzIlQTBCeSUyMGNvbnRpbnVpbmclMkMlMjB5b3UlMjBhY2NlcHQlMjB0aGUlMjBwcml2YWN5JTIwcG9saWN5JTNDJTJGbGFiZWwlM0UlM0MlMkZkaXYlM0UlM0NkaXYlMjBjbGFzcyUzRCUyMnRucC1maWVsZCUyMHRucC1maWVsZC1idXR0b24lMjIlM0UlM0NpbnB1dCUyMGNsYXNzJTNEJTIydG5wLXN1Ym1pdCUyMiUyMHR5cGUlM0QlMjJzdWJtaXQlMjIlMjB2YWx1ZSUzRCUyMlN1YnNjcmliZSUyMiUyMCUzRSUwQSUzQyUyRmRpdiUzRSUwQSUzQyUyRmZvcm0lM0UlMEElM0MlMkZkaXYlM0UlM0NiciUyRiUzRSUzQyUyRnAlM0U=[/vc_raw_html][/vc_column][/vc_row]
No Result
View All Result
  • Contact Us
  • Homepages
  • Business
  • Guide

© 2024 APPROX FOUNDATION - The Crypto Currency News