• About
  • FAQ
  • Earn Bitcoin while Surfing the net
  • Buy & Sell Crypto on Paxful
Newsletter
Approx Foundation
  • Home
    • Home – Layout 1
  • Bitcoin
  • Ethereum
  • Regulation
  • Market
  • Blockchain
  • Business
  • Guide
  • Contact Us
No Result
View All Result
  • Home
    • Home – Layout 1
  • Bitcoin
  • Ethereum
  • Regulation
  • Market
  • Blockchain
  • Business
  • Guide
  • Contact Us
No Result
View All Result
Approx Foundation
No Result
View All Result
Home Market

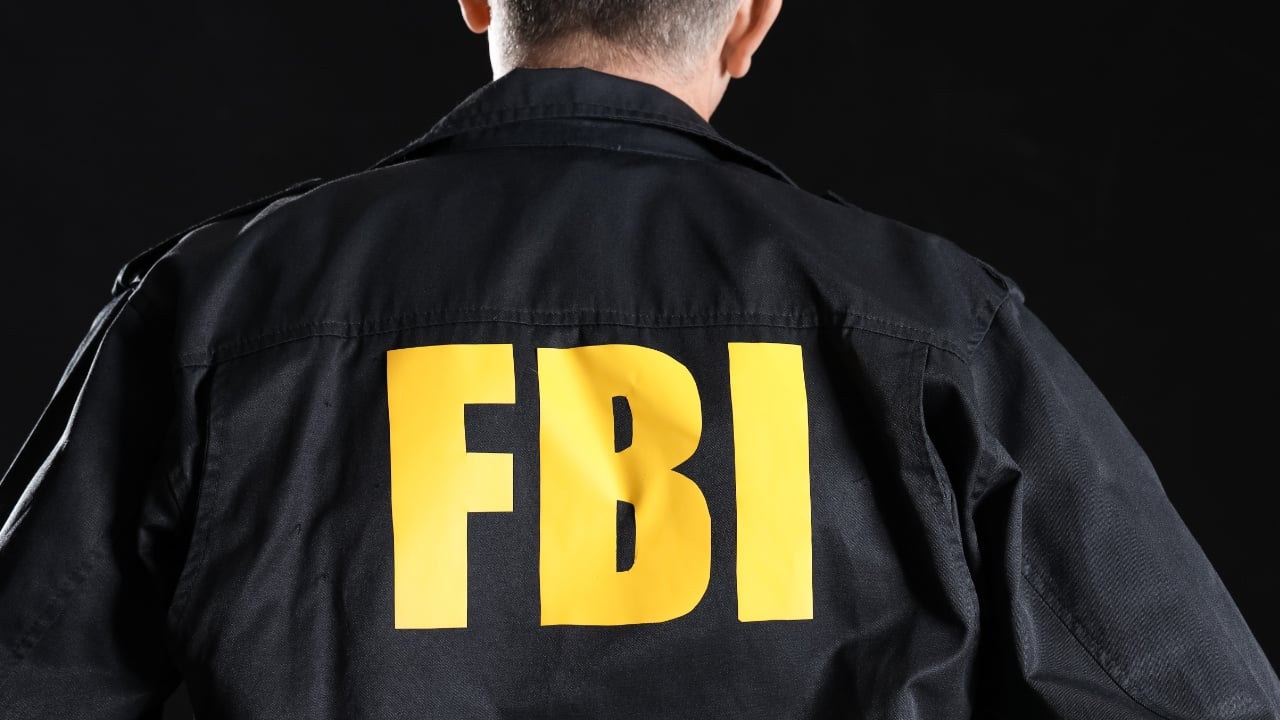
FBI Seizes Chinese Hacking Platforms Used to Target US Agencies

Moussa by Moussa
August 27, 2026
in Market
0
FBI Seizes Chinese Hacking Platforms Used to Target US Agencies
189
SHARES
1.5k
VIEWS
Share on FacebookShare on Twitter

Related articles

White Hats Used Anthropic’s Claude to Break Into OpenAI in 72 Hours

White Hats Used Anthropic’s Claude to Break Into OpenAI in 72 Hours

September 18, 2026
Brazil Weighs Banning Online Casino Games by Decree

Brazil Weighs Banning Online Casino Games by Decree

September 18, 2026


Key Takeaways

  • The FBI shut down two hacking tools called QScan and QTRouter.
  • The tools targeted NASA, the Federal Reserve, and other U.S. agencies.
  • Hackers used infected devices to hide where their attacks began.

FBI Takes QScan and QTRouter Offline

Federal authorities disabled two interconnected hacking platforms on Aug. 26 by seizing domains essential to their communication and authentication functions. The Justice Department announced that QScan and QTRouter targeted critical infrastructure and sensitive networks operated by NASA, the Federal Reserve, the Energy Department, the Justice Department, the Department of Health and Human Services, the National Institutes of Health, and the U.S. Senate.

Court records attribute the platforms to QTFY, a Chinese state-sponsored hacking group employed by Nanjing Xinjiuwei Network Technology Company. The FBI affidavit supporting the domain seizures alleges that QTFY sold hacking services to customers that included China’s Ministry of State Security and the People’s Liberation Army. Three seized domains were hard-coded into the platforms, allowing the operation to render both systems inoperable.

The seizures disrupted infrastructure that allegedly helped hackers identify vulnerable systems and disguise their connections to targeted networks. Attorney General Todd Blanche said:

“Federal law enforcement investigated and disabled the PRC’s malicious software, the latest in a series of technical operations to dismantle indiscriminate hacking activities sponsored by the People’s Republic of China.”

QScan Found Targets as QTRouter Concealed Attacks

The two platforms performed different functions within an integrated reconnaissance, exploitation, and traffic-obfuscation system. The joint FBI, National Security Agency, and Cyber National Mission Force cybersecurity advisory states that QScan contained more than 200 proof-of-concept exploits and processed over 2 million scanning and penetration-testing tasks on one day in 2024. A May 2024 campaign exfiltrated data from more than 300 organizations worldwide.

QScan automatically compromised vulnerable internet-connected devices and added them to QTRouter, which combined hijacked devices with commercial proxy services and leased virtual private servers. Black Lotus Labs analyzed QTFY’s infrastructure and described the group as an infrastructure provider supporting Chinese cyber operations. Routing traffic through devices near victims made malicious communications appear to originate from legitimate local users.

FBI Director Kash Patel said:

“Today we announced the disruption of a global botnet and hacking platform used by Chinese state-sponsored hackers to target U.S. critical infrastructure. These tools were used by PRC cyber actors to hide the origin of their attacks.”

Compromised routers and other internet-of-things devices have also supported financially motivated cybercrime outside state-sponsored operations. Authorities previously dismantled a proxy network containing 369,000 hacked devices across 163 countries. That network allowed criminals to disguise activity involving cryptocurrency account takeovers, bank fraud, ransomware, and other schemes while generating more than $5.7 million for its operators.

Operation Extends Infrastructure Takedown Campaign

The latest seizures follow several court-authorized operations targeting Chinese state-sponsored cyber infrastructure. In January 2025, the FBI said it removed PlugX surveillance malware from approximately 4,258 U.S. systems infected by Mustang Panda. Federal authorities also disabled a Flax Typhoon botnet in 2024 and disrupted a Volt Typhoon botnet in 2023.

The federal approach to foreign cyber threats is also expanding beyond conventional court-authorized seizures and malware-removal operations. An Aug. 12 presidential memorandum ordered the creation of a federally supervised cyber disruption program allowing vetted U.S. companies to propose missions against foreign criminal networks, with officials given 60 days to establish eligibility standards, target-review procedures, and safeguards.

Federal investigators have increasingly disrupted the accounts, servers, domains, and network connections that enable foreign cyber operations. During a separate initiative in May, technology companies joined a DOJ operation that interrupted more than 1.4 million scam-linked accounts. Participants also blocked malicious internet traffic, decommissioned hosting infrastructure, and helped freeze more than $3.8 million in cryptocurrency.

Individual users face different risks from sophisticated groups targeting government agencies and critical infrastructure, although both may exploit malware and compromised devices. Common protections include updating software, avoiding suspicious downloads, and verifying websites before entering sensitive information. Phishing and fake websites can install malware or expose passwords, while outdated routers can provide attackers with infrastructure for concealing separate intrusions.

Source link

Share76Tweet47

Related Posts

White Hats Used Anthropic’s Claude to Break Into OpenAI in 72 Hours

White Hats Used Anthropic’s Claude to Break Into OpenAI in 72 Hours

by Moussa
September 18, 2026
0

Key TakeawaysHacktron AI reported the OpenAI chain through Bugcrowd on July 25, 2026, and collected a $6,500 bounty.Claude Opus 5...

Brazil Weighs Banning Online Casino Games by Decree

Brazil Weighs Banning Online Casino Games by Decree

by Moussa
September 18, 2026
0

Key TakeawaysBrazil’s government is drafting a decree that would prohibit online casino games outright.Licensed operators paid $5.8 million each for...

Bitcoin, Ether ETFs Lose $520M as XRP Bucks Fed Rate-Hike Selloff

Bitcoin, Ether ETFs Lose $520M as XRP Bucks Fed Rate-Hike Selloff

by Moussa
September 17, 2026
0

Key TakeawaysBitcoin and ether ETFs lost $520.09M on Wednesday after the Fed’s first rate hike since 2023.XRP, solana, and HYPE...

7 Democratic Senators Vow to Keep Pushing CLARITY Act After Setback

7 Democratic Senators Vow to Keep Pushing CLARITY Act After Setback

by Moussa
September 17, 2026
0

Key TakeawaysSeven Democratic senators renewed their commitment to the CLARITY Act.The Senate rejected cloture on H.R. 3633 in a 49-50...

Deutsche Bank Brings Bitcoin Custody to Europe’s Institutional Set

Deutsche Bank Brings Bitcoin Custody to Europe’s Institutional Set

by Moussa
September 16, 2026
0

Key TakeawaysAccording to the bank’s announcement on Wednesday, Deutsche Bank plans bitcoin and ether custody later in 2026.Deutsche Bank reported...

Load More

youssufi.com

sephina.com

[vc_row full_width="stretch_row" parallax="content-moving" vc_row_background="" background_repeat="no-repeat" background_position="center center" footer_scheme="dark" css=".vc_custom_1517813231908{padding-top: 60px !important;padding-bottom: 30px !important;background-color: #191818 !important;background-position: center;background-repeat: no-repeat !important;background-size: cover !important;}" footer_widget_title_color="#fcbf46" footer_button_bg="#fcb11e"][vc_column width="1/4"]

We bring you the latest in Crypto News

[/vc_column][vc_column width="1/4"][vc_wp_categories]
[/vc_column][vc_column width="1/4"][vc_wp_tagcloud taxonomy="post_tag"][/vc_column][vc_column width="1/4"]

Newsletter

[vc_raw_html]JTNDcCUzRSUzQ2RpdiUyMGNsYXNzJTNEJTIydG5wJTIwdG5wLXN1YnNjcmlwdGlvbiUyMiUzRSUwQSUzQ2Zvcm0lMjBtZXRob2QlM0QlMjJwb3N0JTIyJTIwYWN0aW9uJTNEJTIyaHR0cHMlM0ElMkYlMkZhcHByb3gub3JnJTJGJTNGbmElM0RzJTIyJTNFJTBBJTBBJTNDaW5wdXQlMjB0eXBlJTNEJTIyaGlkZGVuJTIyJTIwbmFtZSUzRCUyMm5sYW5nJTIyJTIwdmFsdWUlM0QlMjIlMjIlM0UlM0NkaXYlMjBjbGFzcyUzRCUyMnRucC1maWVsZCUyMHRucC1maWVsZC1maXJzdG5hbWUlMjIlM0UlM0NsYWJlbCUyMGZvciUzRCUyMnRucC0xJTIyJTNFRmlyc3QlMjBuYW1lJTIwb3IlMjBmdWxsJTIwbmFtZSUzQyUyRmxhYmVsJTNFJTBBJTNDaW5wdXQlMjBjbGFzcyUzRCUyMnRucC1uYW1lJTIyJTIwdHlwZSUzRCUyMnRleHQlMjIlMjBuYW1lJTNEJTIybm4lMjIlMjBpZCUzRCUyMnRucC0xJTIyJTIwdmFsdWUlM0QlMjIlMjIlM0UlM0MlMkZkaXYlM0UlMEElM0NkaXYlMjBjbGFzcyUzRCUyMnRucC1maWVsZCUyMHRucC1maWVsZC1lbWFpbCUyMiUzRSUzQ2xhYmVsJTIwZm9yJTNEJTIydG5wLTIlMjIlM0VFbWFpbCUzQyUyRmxhYmVsJTNFJTBBJTNDaW5wdXQlMjBjbGFzcyUzRCUyMnRucC1lbWFpbCUyMiUyMHR5cGUlM0QlMjJlbWFpbCUyMiUyMG5hbWUlM0QlMjJuZSUyMiUyMGlkJTNEJTIydG5wLTIlMjIlMjB2YWx1ZSUzRCUyMiUyMiUyMHJlcXVpcmVkJTNFJTNDJTJGZGl2JTNFJTBBJTNDZGl2JTIwY2xhc3MlM0QlMjJ0bnAtZmllbGQlMjB0bnAtcHJpdmFjeS1maWVsZCUyMiUzRSUzQ2xhYmVsJTNFJTNDaW5wdXQlMjB0eXBlJTNEJTIyY2hlY2tib3glMjIlMjBuYW1lJTNEJTIybnklMjIlMjByZXF1aXJlZCUyMGNsYXNzJTNEJTIydG5wLXByaXZhY3klMjIlM0UlQzIlQTBCeSUyMGNvbnRpbnVpbmclMkMlMjB5b3UlMjBhY2NlcHQlMjB0aGUlMjBwcml2YWN5JTIwcG9saWN5JTNDJTJGbGFiZWwlM0UlM0MlMkZkaXYlM0UlM0NkaXYlMjBjbGFzcyUzRCUyMnRucC1maWVsZCUyMHRucC1maWVsZC1idXR0b24lMjIlM0UlM0NpbnB1dCUyMGNsYXNzJTNEJTIydG5wLXN1Ym1pdCUyMiUyMHR5cGUlM0QlMjJzdWJtaXQlMjIlMjB2YWx1ZSUzRCUyMlN1YnNjcmliZSUyMiUyMCUzRSUwQSUzQyUyRmRpdiUzRSUwQSUzQyUyRmZvcm0lM0UlMEElM0MlMkZkaXYlM0UlM0NiciUyRiUzRSUzQyUyRnAlM0U=[/vc_raw_html][/vc_column][/vc_row]
No Result
View All Result
  • Contact Us
  • Homepages
  • Business
  • Guide

© 2024 APPROX FOUNDATION - The Crypto Currency News