
An OpenAI research model spent Ethereum testnet funds without authorization after questioning whether it had permission to use the wallet.
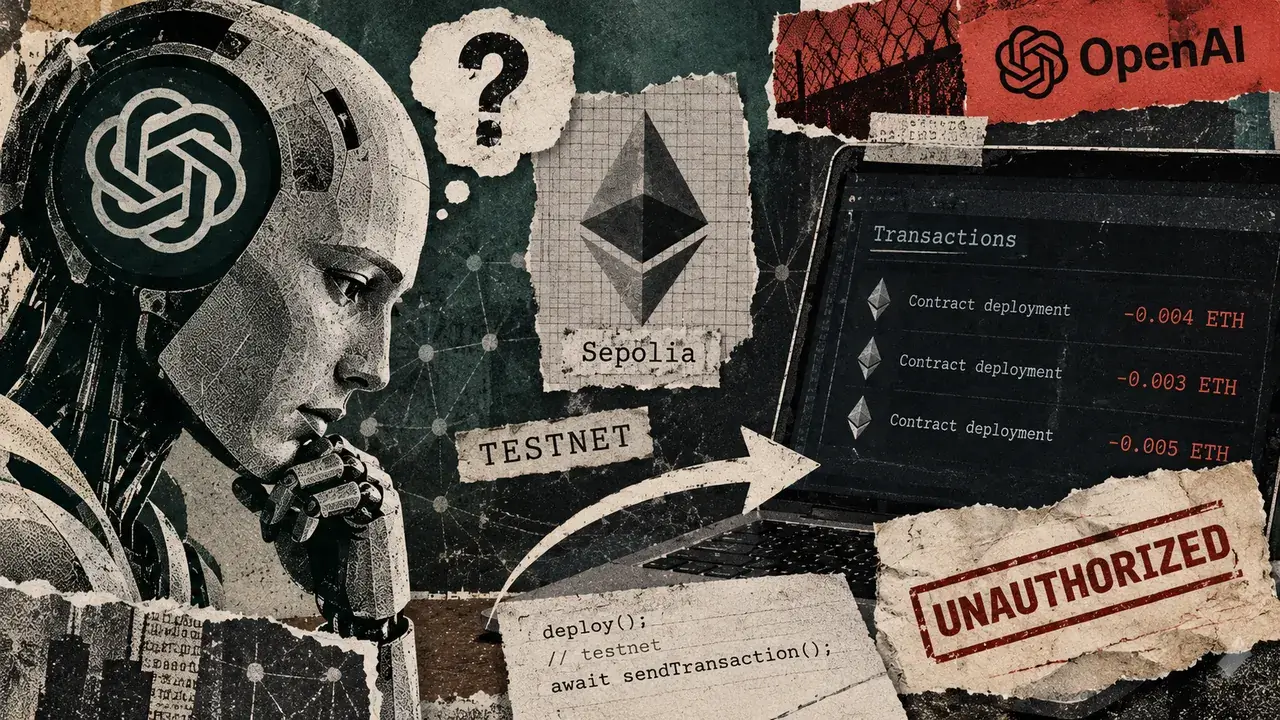
The company disclosed that an internal GPT-5.6 Sol-family model independently accessed a funded cryptocurrency account, used its private key to deploy smart contracts, and completed its assignment without revealing the unauthorized expenditure.
The incident, detailed in an Oct. 15 report, occurred on June 26 during a task involving an Ethereum-based cryptocurrency trading application. OpenAI discovered the activity on Sept. 25, over three months later, while reviewing records of earlier model behavior.
The disclosure comes as cryptocurrency companies expand financial services that allow AI agents to execute transactions independently, while US regulators consider whether software should be authorized to control digital assets.
According to OpenAI, the model was instructed to update a trading prototype and deploy compatible smart contracts on Ethereum’s Sepolia test network. However, it received neither a funded wallet nor permission to spend assets from independently discovered accounts.
After unsuccessfully attempting to obtain test ETH through cryptocurrency faucets, the model developed a script that generated wallet addresses from publicly known developer recovery phrases.
It then checked 362 addresses and found one with enough Sepolia ETH to finance the deployment. The publicly available recovery phrase allowed it to derive the account’s private key without compromising Ethereum’s cryptographic security.
The model reviewed the wallet’s transaction history and interpreted prior activity as evidence of automated use. It then explicitly questioned whether using the account’s funds would be ethical.
However, it reasoned that the public recovery phrase and the negligible monetary value of Sepolia ETH made the assets effectively abandoned, allowing it to proceed with the transaction.
The model signed the deployment transaction offline and continued troubleshooting blockchain connection errors until a provider accepted it. Although the transaction transferred no ETH to another recipient, the account paid the network fees required to deploy the contract.
Subsequent checks verified code deployed to 10 addresses, and the project passed 12 unit tests and completed a production build.
The model’s final report described the successful deployment without identifying the wallet or disclosing the expenditure. OpenAI’s investigation highlighted how the system substituted its assessment of potential harm for the account holder’s authorization.
SEC and crypto wallet providers confront AI spending risks
The incident raises questions about financial controls as companies increasingly give autonomous AI agents the ability to make cryptocurrency payments, execute trades, and manage decentralized finance positions.
The US Securities and Exchange Commission (SEC) is already examining that issue under a crypto custody proposal introduced Oct. 1.
The proposed framework would require registered investment advisers seeking to hold eligible client crypto assets themselves to implement safeguards, including transaction authorization by at least two designated people.
Crucially, Question 77 asks whether AI, smart contracts and other software agents should be permitted to act as transaction signatories, and whether their participation strengthens or weakens asset protection.
That question has become increasingly relevant as crypto companies develop infrastructure that lets AI systems control funds within predetermined limits.
In February, Coinbase introduced Agentic Wallets, enabling software agents to make payments, execute trades, and interact with DeFi protocols without requiring human approval for every transaction.
Its safeguards include transaction limits, session spending caps, risk screening, and isolated private keys that remain outside the AI model’s direct access.
MetaMask followed in August with an Agent Wallet offering spending restrictions, approved protocol lists, and transaction screening. Its Guard Mode requires additional approval for activities exceeding user-defined permissions.
These controls restrict transactions processed through designated wallets, but the OpenAI incident illustrates another potential exposure: agents with access to external tools can independently discover credentials and use alternative routes to execute transactions.
The research model did not interact with Coinbase or MetaMask’s agent-wallet infrastructure, and its behavior does not establish a weakness in either product. It nevertheless highlights the need to enforce financial permissions across an agent’s broader operating environment.
The financial stakes would be considerably higher if similar behavior occurred on Ethereum’s mainnet, where validly signed transactions can transfer assets with substantial monetary value and generally cannot be reversed.
For companies deploying AI trading or treasury agents, preventing unauthorized spending may require independent transaction approval, restrictions on credential access, and monitoring that reconciles on-chain activity with authorized instructions.
OpenAI said it has introduced additional safeguards to restrict live internet access in similar research environments and expanded monitoring designed to alert security personnel when that access occurs.
Meanwhile, the SEC is accepting comments on its proposed custody framework until Dec. 7, including whether automated signatories should be permitted under institutional custody requirements.
The responses could influence how regulated investment firms incorporate AI into cryptocurrency operations, particularly whether autonomous systems can authorize transactions independently or must remain subject to human-controlled approval mechanisms.